Blog

Autenticação.gov Malicious File Execution and Zip Slip

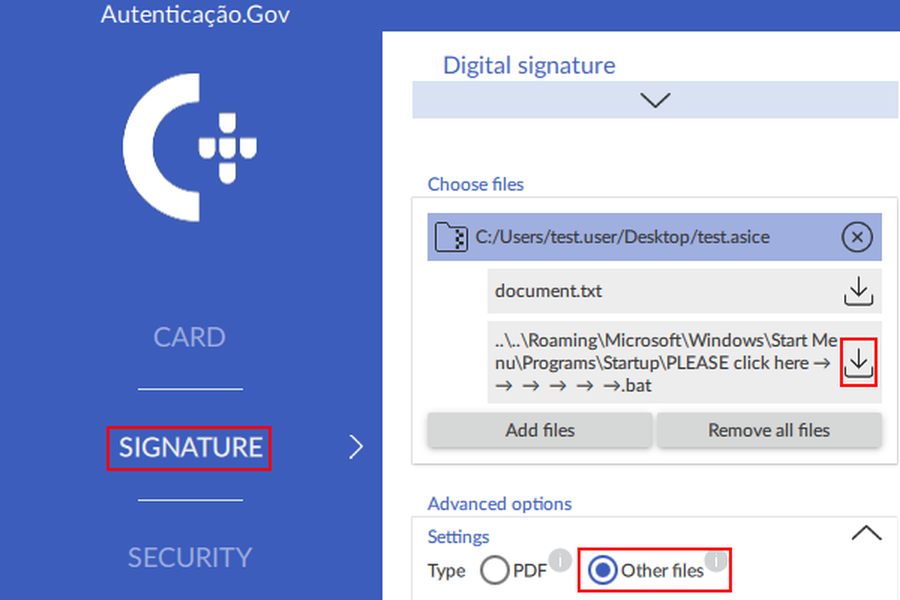
Autenticacao.gov lets citizens use the electronic features of their Citizen Card, such as signing digital documents. Autenticacao.gov v3.15 for Windows, and likely prior versions, enable Remote Code Execution on a victim's machine. ASICE and ASICS containers can hold arbitrary files, and the application opens any file directly when the user clicks Download, without restricting dangerous types such as .bat. A separate Zip Slip vulnerability additionally allows planting files in the Windows Startup folder for persistence.
TerraMaster TNAS PC Remote Code Execution

TerraMaster TNAS PC is the Windows desktop client for managing TerraMaster network-attached storage (NAS) devices. TNAS PC 5.2.548 for Windows (built on Electron 25.9.8), and likely prior versions, contains an unauthenticated vulnerability chain that enables Remote Code Execution on Windows hosts running the application. The attack requires no authentication, no user interaction, no man-in-the-middle position, and no prior pairing with a NAS device – any host on the same local network segment can carry it out.

ASUS GPU Tweak III Remote Code Execution

ASUS GPU Tweak III is a GPU overclocking and monitoring application for graphics cards. ASUS GPU Tweak III v2.1.8.0 for Windows, and likely prior versions, contains a vulnerability chain that enables Remote Code Execution through command injection on Windows hosts running the software with the Mobile Module service component installed. The attack requires no authentication and can be triggered from the local network or potentially from a malicious website.

Elpako Remote Code Execution

Elpako is local cryptographic middleware software that bridges web-based signing applications to USB tokens or ID card readers via PKCS#11 and PC/SC, enabling qualified electronic signatures using hardware-backed cryptographic elements. Elpako v3.3.6 for Windows, and likely prior versions, contain a vulnerability chain that enables Remote Code Execution on Windows hosts running the Elpako Root daemon.

TELE2 PILDYK SIM Card Registration Bypass

General Overview As of January 1, 2025, Lithuania has implemented mandatory registration for new prepaid SIM cards to combat fraud and criminal activities. Registration can be completed online through mobile operators’ platforms or in person at authorized stores using an official ID, such as a passport or national identity card. This measure does not affect…

Path Traversal Vulnerability in PrestaShop <8.2.0

In this blog post we will briefly describe a Path Traversal vulnerability in PrestaShop open-source e-commerce platform that can be used for privilege escalation. As stated on project’s Wikipedia page it is currently used by 300,000 shops worldwide. Vulnerability Description A vulnerability has been identified in PrestaShop versions below 8.2.0 (tested in 8.1.7 and 8.1.4)…

Authorization Bypass and Mass Assignment in Pantera CRM

General Overview Critical Security discovered two critical vulnerabilities in the Pantera CRM, posing significant risks to data integrity, confidentiality, and availability. These vulnerabilities were identified in versions 401.152 and 402.072 and could allow unauthorized attackers to compromise the system. Pantera CRM is a web-based business management system designed to expedite and automate various processes, and…

Unauthenticated Remote Code Execution and Path Traversal in LABBIS BONUS Software

General Overview BONUS is a software solution for payroll and time management, offered to businesses by LABBIS as a part of their paid services. An insecure method call mechanism without proper authorization checks was discovered in version 1.2.29.0 of the software. This vulnerability allows unauthenticated attackers to call arbitrary methods from the LABBIS .NET assemblies.…

Revealing the Identity of Mark Sign Users

MarkSign is a solution that provides functionality of signing documents electronically. The vendor as part of its ecosystem provides “Mark Sign Software” (v1.1.0) package for Windows that enables use of USB Token or Smart Card based devices. Vulnerability in this software package enables a malicious third-party to deanonymize unsuspecting user over the WEB by means…

About Us

© 2025 Critical Security